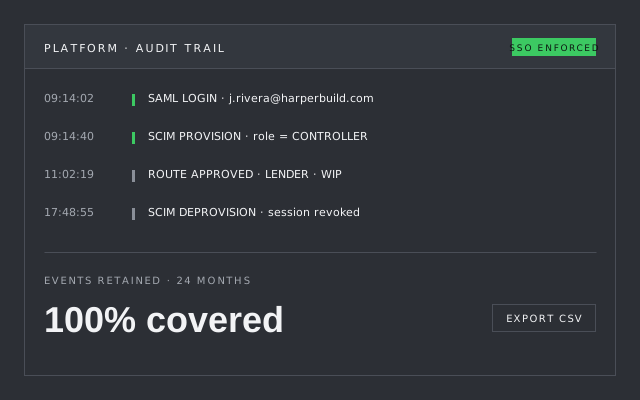
Contractors working inside owner and lender programs are increasingly asked to prove who can reach financial data and how that access is revoked. This release answers that with configuration rather than a written policy.
What shipped
- SAML 2.0 single sign-on. Works with Okta, Entra ID, and any SAML-compliant provider. Once enforced for a workspace, password sign-in is disabled for every member outside the break-glass owner account.
- SCIM provisioning. Users and roles are created, updated, and deactivated from your identity provider. A deprovision revokes active sessions immediately rather than at next token expiry.
- Audit trail with export. Sign-ins, role changes, route approvals, and every consent granted or revoked through Interchange are retained for 24 months and exportable as CSV.
Notes
SSO enforcement is available on Program and Enterprise workspaces. Turn it on under Settings → Security; we recommend running SCIM in provision-only mode for a full cycle before enabling deprovisioning.